AI Enhances Online Dating Safety Without Replacing Humans
A February 2025 study from iProov, a leading biometrics vendor, revealed shocking results: only two subjects made zero errors in identifying real versus fake images or videos. This highlights the inadequacy of current detection tools for advanced generative AI models like deepfakes and injection attacks. The article discusses how traditional methods of user safety checks (photo scrutiny, story…
Key points
- Only two subjects made zero errors in identifying fake content out of 2,000 tested
- Deepfakes now account for one in five biometric fraud attempts
- Current detection tools are failing due to rapid progress in generative AI models
AI Can Help Us Find Real People, Not Replace Them
Unite.AI · 15 September 2026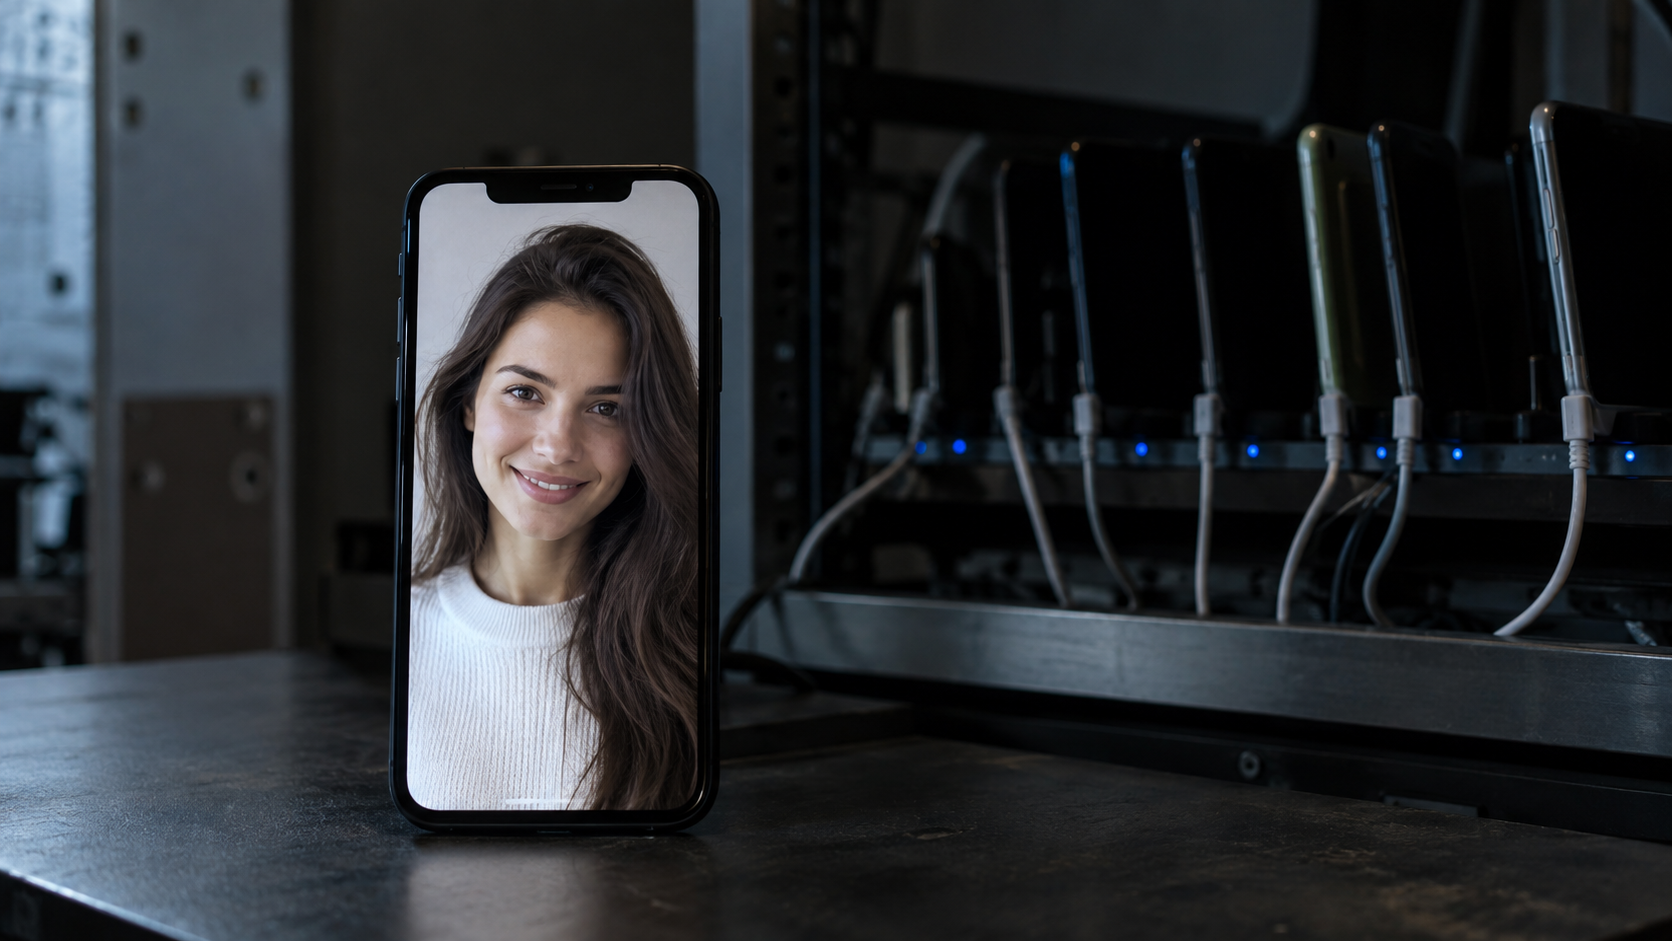
A fake image fools even the sharpest eyes, but fake behavior that the platform sees should not.
For the past twenty years, the online dating industry taught user safety as a straightforward checklist. We advised users to scrutinize the photo, check the person’s story for consistency, or insist on a video call before agreeing to meet. That guidance, once the gold standard of digital safety, is completely obsolete today.The definitive proof arrived in a February 2025 study from iProov, a leading biometrics vendor. Researchers asked 2,000 subjects in the UK and the US to label various items — using both images and videos — as either real or synthetic. The results were astonishing: only two subjects made zero errors. That is a mere 0.1 percent of the people tested, meaning the other 1,998 made at least one mistake. High confidence combined with a high error rate is a dangerous mixture for consumers. And the fraudsters are more than ready to exploit it.According to the Entrust 2026 Identity Fraud Report, deepfakes now account for one in five biometric fraud attempts. Deepfaked selfies rose 58 percent in 2025, and injection attacks increased by 40 percent year over year. Expecting an everyday user to beat a highly advanced generative AI model at visual perception is an abdication of responsibility; it transfers the risk directly from the platform to the customer.
Fraud is No Longer About Finding Fake Pictures
The reality is that current detection tooling is failing because it runs object-level tests on one object at a time. One test asks whether a specific image was generated by AI. Another asks whether a document is forged, while a third asks whether the text in a message was machine-written. The problem is that each of these test decays quickly. As generative-model progress continuously raises output quality, prior responses and detection methods become dated or obsolete almost overnight.
A much better approach replaces single-signal appearance with the joint fit of many signals. Our method scores the relationships between various dimensions of a user’s presence. One dimension of signal is what a device looks like to our system. Another is where a user’s session is arriving from. A third is how the account actually behaves. All of this leads to human review when the system flags indicators of possible fraud.
The United Nations Office on Drugs and Crime, in its Transnational Organized Crime Threat Assessment for South-East Asia 2026, estimated 2025 online-scam losses at between US$88.3 billion and US$114.1 billion in the reported areas alone. Industrial fraud at this scale runs on speed and volume. Any single piece of information can be easily faked, but faking all of them consistently — across multiple accounts that are continuously being knocked down by the platform — becomes far too burdensome to maintain. Every layer of friction we introduce raises the per-account cost of the fraud business until their profit margin reaches zero.
This is where AI truly earns its keep. While forgery detection has improved with new technologies, the improved ability to identify coincident factors indicating fraud — and leading to earlier intervention — is vastly better for our users. When a user’s indicators disagree, their true intention is exposed. An honest member, a fraudster, and a visitor with another purpose might all share identical photos and near-identical opening lines. Their combined indicators, however, will differ and tell a completely different story. The way people reply, how quickly they respond, how they escalate the conversation, what they ask about, and which conversations are abandoned all paint a picture. Identity can be a flawlessly generated lie, but conduct will always reveal bad intentions.
The Information Asymmetry: Platforms Know Things Users Can’t
The Federal Trade Commission reported in 2026 that romance-scam losses in 2025 rose 22 percent over 2024, reaching approximately $1.5 billion. Among those who identified how they were contacted, about 60 percent said their initial contact came on a social media platform.
There is a massive information gap in our industry. Platforms see the same categories of signal, but they almost certainly can also see the login country and account age, for example. All members see is a smile and a carefully crafted paragraph that cleverly mixes in something from their profile. Platforms have the power to act on this hidden data, using it to engineer a safer environment, or disclose it so members can act accordingly. Unfortunately, most of the industry does neither.
The industry’s inaction often has to do with the complex trade-offs related to user privacy. The costly half of this equation is taking action. There are two routes to establishing trust: the slow route is reputation, and the fast route is verification. Verification creates friction. The industry overwhelmingly wants speed, volume, and low friction, which explains its chronic under-verification.
However, solutions are emerging. An August 2024 preprint on arXiv proposed “personhood credentials“. The 32 authors from institutions like OpenAI, Microsoft, MIT, Oxford, and Harvard proposed a privacy-preserving credential that allows someone to prove to a service that they are a real person without revealing their underlying identity. Their argument is that CAPTCHAs are inadequate and anomaly detection is rapidly eroding against capable AI. They are right. Dating is one of the places the consequences of this erosion land the hardest because the core product being sold is trust itself.
Engineering a Better Community Standard
The same signals that help identify possibly criminal conduct can also help identify other types of bad acts. Reading intention extends far beyond just stopping fraud. Not every bad actor on a website is a criminal. A user who is unpleasant may not be breaking the law, and a relationship treated as a transaction may not be fraud. Treating people with contempt doesn’t lead to a federal indictment. But these behaviors profoundly degrade the community. Worse, they are too often invisible to systems that rely entirely on member reports for their enforcement programs.
The industry has traditionally drawn the line at illegality: screen for fraud and minors, remove what the law strictly requires, and treat the rest as a matter between consenting adults. I know of no other dating site that uses AI to help identify transactional behavior and actively stop it. Our Stop@Send feature evaluates the sender’s outgoing message as it is being sent. It looks for deeper meaning rather than simply comparing the content to a static keyword list. Most of the time, the response is an explanation delivered to the sender, telling them precisely why the message is inappropriate for the community.
This isn’t free, of course. Interrupting member conversations creates friction, which is unsurprisingly a cost we actively choose to absorb. But our standards are best established by what conduct is actually permitted on our platform, not by what is published on an unenforced community guidelines page. A platform that will not inconvenience a bad actor has no business calling itself a community.
The Challenge to the Industry
The market right now is racing to have AI replace people: we see the rise of AI companions, AI-generated profiles, and flirting agents. I firmly think that direction is a dead end. It optimizes entirely for engagement but delivers absolutely nothing but that. Our approach is fundamentally different. We are using AI to help get rid of the bad actors, to hold members accountable to each other, and to help them treat each other in ways that are more likely to lead to meaningful, real-world relationships.
Lists of red flags to avoid have lost their value. The signals that used to give scammers away are the exact features that generative models have learned to eliminate, creating an arms race we are perpetually locked in. Other than the First Rule — don’t ever send money to anyone you do not know and have not met in person, which everyone should follow — the key question isn’t about the photograph anymore. It’s about the platform, and what they’re doing with what they know that their users don’t.
A platform that has good responses to that challenge is actively engineering for trust. A platform that doesn’t is asking its members to do more work at a 0.1 percent success rate just to protect themselves.
I put this challenge to every platform, including my own. I expect the answers to be honest and complete. The technology to close this gap exists right now. Fraud persists because stopping it means surrendering the massive growth that comes through the giant front door of effortless signup. This is a business decision rather than a technical limitation. And the platforms that decide correctly hold the only asset that matters for this discussion: their members’ trust.
This text was published by Unite.AI and written by Brandon Wade, Founder & Co-CEO, Seeking.com. It is reproduced here with attribution so you can read it in full; the rights remain with the publisher. Read it at the source ↗
The headline, key points and digest above were generated by Digest AI's editorial model from the linked sources. Automated summaries can contain errors: the sources are the record. Spotted a mistake? Tell us.
Comments
via GitHub Discussions